DATA PROTECTION & COMPLIANCE · DATA PROTECTION
Data Protection in Dresden — GDPR Concepts, Audits and Ongoing Support
Data protection concepts, audits, records of processing activities and technical and organisational measures. We make GDPR practical rather than producing 80-page PDFs that nobody reads.
Typical Starting Points
- You are unsure whether your cookie solution actually complies with GDPR.
- There is no external data protection officer, or the internal role is unclear.
- Records of processing activities and technical and organisational measures are outdated or missing.
- Nothing would be documented if the supervisory authority received a complaint.
The Focus of Data Protection
Consulting starts with existing processing activities, responsibilities and documentation. Audits, processing records and technical and organisational measures are reviewed against actual practice. The competence hub explains their relationship with digital systems and workflows.
The Service in Detail
Assessment & Documentation
- GDPR Audit
- An inventory of all processing activities, risks and gaps, with clear priorities.
- Records of Processing Activities
- Structured documentation of all processing activities — understandable and ready for audits.
- TOMs
- Documented and verifiable technical and organisational measures.
Data Protection Officer
- External Data Protection Officer
- We act as your external data protection officer — practical and approachable.
Training & Incident Procedures
- Employee Training
- Live training or e-learning with documented attendance.
- Data Breach Response
- Emergency procedures, reporting obligations and documentation — prepared before an incident occurs.
The Approach
Audit
Inventory, risk analysis and priorities.
Planning
A data protection roadmap, records of processing activities and technical and organisational measures.
Implementation
Technical measures, contracts, data processing agreements and privacy policies.
Training
Raise employee awareness and document participation.
Ongoing Operations
External data protection officer, annual reviews and responses to enquiries and incidents.
The Service Within Its Competence Area
The competence hub explains the wider connections. Data Protection focuses here on the specific task.
Data Protection & Compliance →Technical and Practical Foundations
- Records of Processing Activities
- Data Processing Agreement
- Cookie Consent
- TOMs
- ePrivacy
- TTDSG
How the Elements Connect
- Processing
- Documentation
- Measures
- Review
Project, Handover and Ongoing Work
A Defined Project
In a defined project, we review processing activities, documentation and organisational responsibilities and agree the scope around the existing environment.
After Implementation
For the continuing work on Data Protection, the existing process includes: External data protection officer, annual reviews and responses to enquiries and incidents.
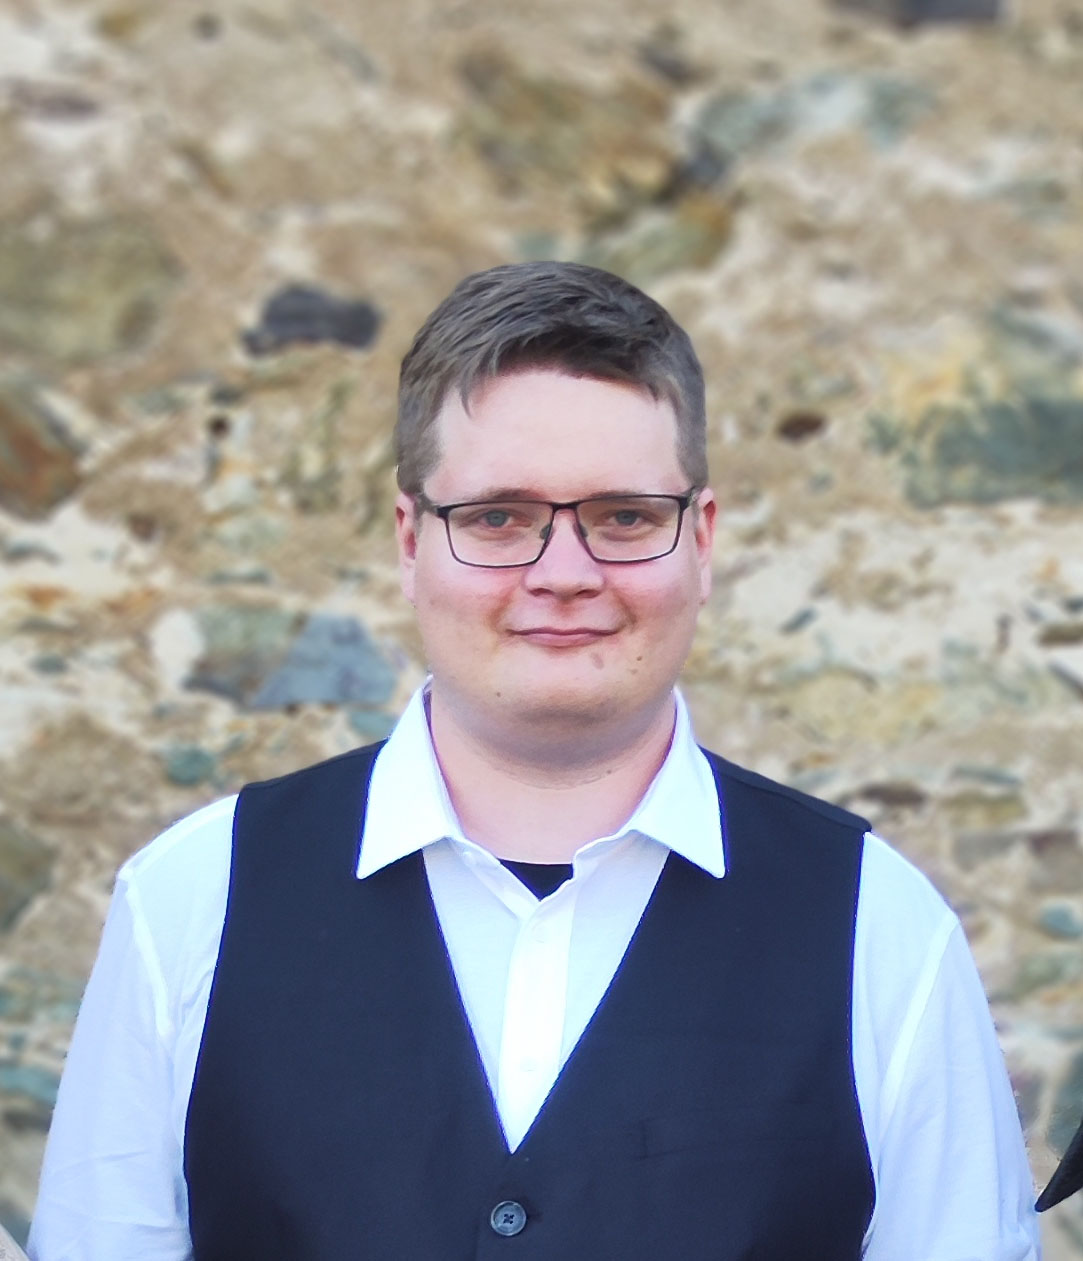
Scott Nowak. Direct Collaboration on Data Protection.
I am Scott Nowak, your direct contact for Data Protection. We discuss processing activities, documentation and organisational responsibilities and connect the requirements with their implementation.
More About Scott →Questions About Data Protection
Do we need a data protection officer?
Appointment is mandatory from 20 people who regularly process personal data, or if you carry out extensive profiling or tracking. We assess this based on your processing activities — appointment can also be worthwhile where it is not mandatory.
How much does an external data protection officer cost?
Typically €180–450 per month for SMEs in Dresden with 20–100 employees, depending on the sector and extent of processing. The initial audit is offered at a fixed price.
Does a cookie banner automatically comply with GDPR?
Rarely. Many implementations look polished but set tracking cookies before consent or fail to record consent in a verifiable way. We audit against TTDSG and GDPR and configure the solution around these requirements.
What happens in a data breach?
A 72-hour reporting deadline to the supervisory authority, notification of affected individuals where required and complete documentation. We establish an emergency procedure with you and support you during an incident.
Do you also write website privacy policies?
Yes, but we do not copy templates. We scan your website for trackers, list all processors and write an accurate, readable policy rather than one only lawyers enjoy.
Where do documentation and practice differ?
Describe processing activities, documentation and organisational responsibilities. The existing project brief lets you share your starting point and supporting materials.
Would you like to speak first? →Response time: < 48 h
Project start: typically 2–4 weeks
Within 48 hours on business days.